
Beyond the Front Office: Why the Defense Industrial Base is Racing Against the Clock on CMMC Compliance

WASHINGTON — For the past four consecutive years, the manufacturing sector has stood squarely in the crosshairs of global cyber espionage and digital extortion. According to IBM’s 2025 Threat Intelligence Index, manufacturing remains the single most targeted industry for cyberattacks worldwide. Adversaries are no longer merely targeting corporate email servers or administrative office computers; they are actively hunting for intellectual property, probing for vulnerabilities to disrupt mission-critical operations, and exploiting legacy systems that were never engineered to withstand modern, persistent digital threats.
Nowhere are the stakes higher—or the digital attack surface more complex—than within the Defense Industrial Base (DIB). As the Department of Defense (DoD) phases in its Cybersecurity Maturity Model Certification (CMMC) framework, contractors and subcontractors alike are coming to a stark realization: securing a manufacturing business against cyber threats requires a fundamental rewiring of how physical and digital operations intersect.
Main Facts: The Anatomy of the CMMC Challenge
At its core, CMMC is designed to safeguard Controlled Unclassified Information (CUI) as it flows through the defense supply chain. This information—ranging from highly detailed computer-aided design (CAD) drawings and technical specifications to manufacturing tolerances and material formulas—rarely stays in one place.
Before a critical aerospace or ground-vehicle component ever reaches a prime contractor, the underlying technical data may pass through a labyrinth of systems, servers, and sub-tier suppliers. A single digital blueprint might arrive via secure file transfer from a defense customer, reside on a local engineering server, be modified by a design technician, and ultimately stream directly to the numerical control (NC) equipment on the shop floor used to mill the part.
Understanding this digital breadcrumb trail is the foundational challenge of CMMC. Organizations must map precisely where CUI travels, who has administrative or operational access to it, and which hardware and software systems touch it. This creates an assessment scope that is radically different from simply securing the desktop computers in the corporate front office.
Michael Eaton, executive director of the Missouri Association of Manufacturers (MAM), captures the operational disconnect succinctly.
"Manufacturers are exceptionally good at solving tangible problems," Eaton observes. "If something breaks on the shop floor, it gets fixed. If a process slows production, it gets reworked. Cybersecurity, on the other hand, is invisible. I once had an owner tell me, ‘My nephew dabbles in computers, so I let him handle all the IT stuff.’"
With the rollout of CMMC, that invisible problem is being dragged into the harsh light of objective regulatory compliance.
Chronology: The Evolution to Objective Evidence and Formal Verification
The transition from voluntary guidelines to mandatory third-party assessments marks a profound evolution for defense contractors.
The Era of the Self-Assessment
For years, the standard for safeguarding defense information relied on contractor self-assessments against the National Institute of Standards and Technology (NIST) SP 800-171 framework. While many small- and medium-sized manufacturers made earnest, good-faith efforts to evaluate their security postures, the self-assessment model left vast room for subjective interpretation. Companies regularly scored their own compliance without standardized guidelines on scoping, documentation depth, or the type of rigorous evidence required to back up a score.
The Formal Assessment Reality Check
When organizations transition from self-evaluation to formal audits, the assumptions of compliance often evaporate under scrutiny. Data compiled across early certification efforts reveals an average gap of negative 133 points between a company’s self-assessed score and its evidence-based post-assessment score.
A shortfall of that magnitude is rarely the result of a single missing firewall or a lone technical failure. Instead, points bleed away across dozens of interdependent requirements:
- Documentation Gaps: A technical control may physically exist, but the organization lacks the written policies or configuration logs to prove it operates continuously.
- Operational Drift: A formal policy may dictate how employees handle sensitive data, but day-to-day practices on the floor tell a different story.
- Scoping Errors: Systems that handle or transmit CUI are frequently left outside the defined security boundary during initial internal reviews.
"Most manufacturers are doing a lot of the right things," Eaton notes. "The problem is they don’t realize how much is involved once you look at data flow, documentation, evidence, and how everything connects."
Regulatory Rollout Timeline
The regulatory framework governing this transition has been moving from policy to enforcement:
- Late 2024 to Mid-2025: Final rulemakings and updates to the Defense Federal Acquisition Regulation Supplement (DFARS) codified the mechanics of the CMMC program.
- November 2025: The DoD officially began phasing CMMC requirements into applicable solicitations and contracts, setting off a three-year implementation ladder.
- 2026–2028: Requirements are progressively rolling down through prime contractors to touch every tier of the supply chain handling CUI.
Supporting Data and Operational Scope
Reaching the required level of CMMC readiness is fundamentally an organizational change management project disguised as an IT upgrade. Because CUI touches virtually every corner of a manufacturing enterprise, readiness initiatives inevitably rope in engineering, operations, human resources, executive management, and the production floor.
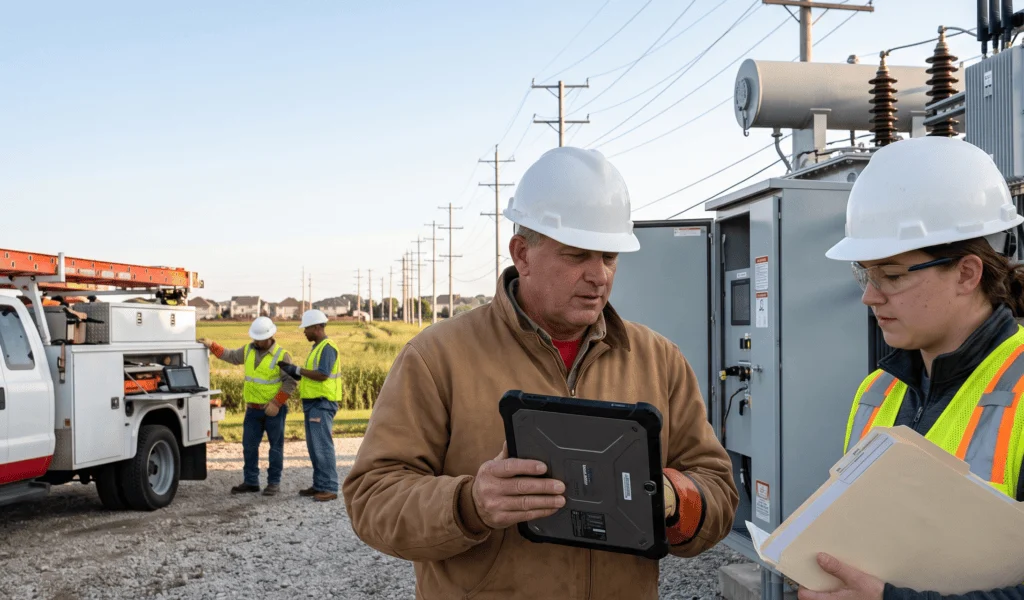
For a sprawling tier-one defense contractor, these responsibilities are divided among dedicated legal, compliance, and cybersecurity departments. For a regional small manufacturer with 50 employees, however, those same sweeping responsibilities often land squarely on the shoulders of a single overworked operations manager or general manager.
"This isn’t something you muscle through after hours," Eaton warns. "Most owners are already spread thin. They don’t have the time or the internal resources to interpret what’s required, let alone to make sure it all gets completed and documented properly."
Depending on a company’s technological baseline, legacy infrastructure, and existing security maturity, achieving compliance can take anywhere from six months to well over a year. Organizations that wait until a critical CMMC clause appears in a lucrative Request for Proposal (RFP) are, by definition, starting too late.
Official Responses and Strategic Guidance
Faced with steep hurdles, industry associations and expert advisors are rushing to establish structured pathways for vulnerable suppliers. Chief among these strategies is the avoidance of premature spending.
Establish the Baseline Before Buying the Fix
A common pitfall for manufacturers is attempting to buy their way out of compliance by purchasing expensive, off-the-shelf security software before conducting a proper diagnostic. If the core vulnerability is an incorrectly defined security boundary or a fundamental misunderstanding of data flows, purchasing another enterprise software license will do little to close compliance gaps.
Industry experts strongly advise initiating a formal gap assessment to establish a clear baseline. For companies lacking dedicated cybersecurity teams, Registered Provider Organizations (RPOs) can step in to interpret requirements, evaluate current network environments, identify deficiencies, and build a prioritized roadmap.
It is vital to note that RPOs assist with preparation and remediation, but they do not perform the official certification audit. When a third-party assessment is legally required for contract award, it must be conducted by an authorized CMMC Third-Party Assessment Organization (C3PAO).
"My advice is always the same," says Eaton. "Don’t try to go it alone. What we do at MAM is connect our members with a vetted RPO."
Because the marketplace for cybersecurity consultants has exploded with vendors of varying quality, manufacturing associations are taking on a gatekeeping role—vetting service providers to protect time-strapped business owners from predatory pricing and ineffective advice. "They meet manufacturers where they are and map a path to the finish line," Eaton adds. "That clarity is what our members need. They don’t need more noise."
Implications for the Defense Industrial Base
The broader business implications of CMMC become starkly apparent when viewed through the lens of modern supplier qualification.
The New Pillar of Supplier Qualification
For decades, qualifying as a defense supplier depended on four traditional pillars:
- Quality: Can you meet exacting product tolerances?
- Cost: Can you produce components competitively?
- Delivery: Can you meet strict deployment schedules?
- Technical Capability: Do you possess the domain expertise required for the program?
CMMC has effectively introduced a fifth non-negotiable pillar: Cybersecurity Readiness.
A manufacturer can possess state-of-the-art machinery, decades of flawless engineering pedigree, and unrivaled delivery records, but none of those strengths will override a CMMC eligibility failure. For suppliers heavily concentrated in the defense sector—where military contracts can represent 80% to 90% of total annual revenue—failing to achieve certification does not merely mean losing a client; it threatens the entire commercial viability of the firm.
Risk for Prime Contractors
The ripple effects extend upward to prime contractors as well. If a specialized sub-tier supplier cannot meet the mandatory cybersecurity threshold, the prime contractor is forced to scramble. Replacing an irreplaceable supplier mid-program introduces severe sourcing bottlenecks, qualification delays, and immense cost overruns. Consequently, primes are aggressively auditing their supply chains to prune non-compliant vendors well in advance of contract deadlines.
The Capacity Crunch
Compounding the challenge is a looming resource bottleneck. Thousands of companies are attempting to navigate the readiness and assessment pipeline concurrently. However, the pool of certified C3PAOs, qualified assessors, and specialized cybersecurity consultants is finite.
As the compliance deadline pressure mounts, manufacturers who delay preparation risk finding themselves at the back of a congested line, competing for scarce expert resources while racing against an unyielding contractual clock.
Legislative Attention on Small Suppliers
Recognizing that cybersecurity mandates do not scale downward with company size, policymakers are beginning to take notice. Small manufacturers face disproportionately high fixed compliance costs relative to their revenue. In response, regional manufacturing groups like MAM are actively lobbying federal and state lawmakers for dedicated funding mechanisms, grants, and low-interest loan programs to help small suppliers absorb the costs of CMMC readiness and secure the DIB supply chain.
Conclusion: Turning the Corner on Compliance
Financial assistance and external consultants can ease the journey, but they cannot eliminate the hard work required internally. Manufacturers have built their reputations on mastering demanding customer specifications, surviving rigorous quality audits, and adapting to shifting industrial requirements.
For CMMC, the transformation ultimately hinges on treating cybersecurity with the same operational rigor as physical manufacturing quality control. Once the digital boundaries are clearly defined, the data flows mapped, and the evidence gathered, manufacturers will find what they always do: a complex problem broken down, tackled, and successfully solved.
The only remaining question is how much work each organization has left to accomplish before the clock runs out.